On this page
Cloud practices ensure secure, cost-effective, and resilient use of cloud services. This practice covers security, architecture, and operational best practices for cloud deployments.
Cloud Security Best Practices
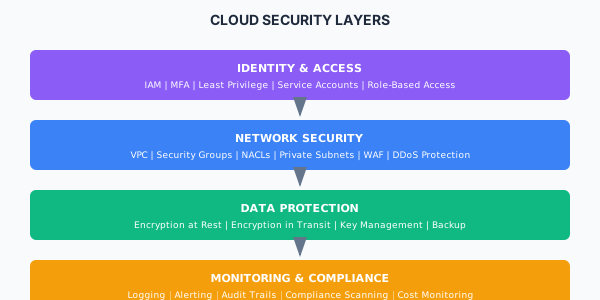
Cloud Security Layers Identity and Access Management
IAM Best Practices
IAM Policy Example (AWS)
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "AllowS3ReadOnly",
      "Effect": "Allow",
      "Action": [
        "s3:GetObject",
        "s3:ListBucket"
      ],
      "Resource": [
        "arn:aws:s3:::my-bucket",
        "arn:aws:s3:::my-bucket/*"
      ],
      "Condition": {
        "StringEquals": {
          "aws:PrincipalTag/Environment": "production"
        }
      }
    }
  ]
}
Service Account Security
# Kubernetes service account with workload identity
apiVersion: v1
kind: ServiceAccount
metadata:
  name: my-app
  annotations:
    # AWS IRSA
    eks.amazonaws.com/role-arn: arn:aws:iam::123456789:role/my-app-role
    # GCP Workload Identity
    iam.gke.io/gcp-service-account: my-app@project.iam.gserviceaccount.com
Network Security
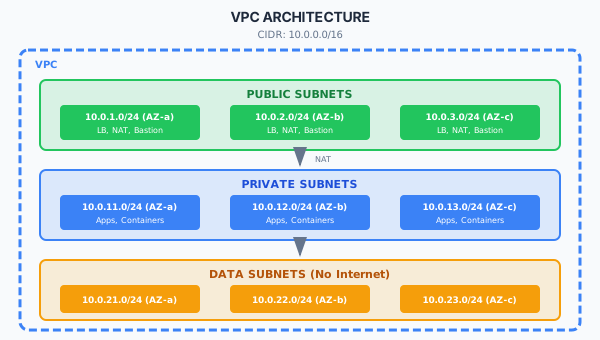
VPC Architecture
VPC Architecture Security Group Rules
# Terraform security group
resource "aws_security_group" "app" {
  name        = "app-sg"
  description = "Security group for application servers"
  vpc_id      = aws_vpc.main.id

  # Allow HTTP from ALB only
  ingress {
    from_port       = 8080
    to_port         = 8080
    protocol        = "tcp"
    security_groups = [aws_security_group.alb.id]
  }

  # Allow all outbound
  egress {
    from_port   = 0
    to_port     = 0
    protocol    = "-1"
    cidr_blocks = ["0.0.0.0/0"]
  }

  tags = {
    Name = "app-sg"
  }
}
Data Protection
Encryption at Rest
KMS Key Policy
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "Enable IAM policies",
      "Effect": "Allow",
      "Principal": {
        "AWS": "arn:aws:iam::123456789:root"
      },
      "Action": "kms:*",
      "Resource": "*"
    },
    {
      "Sid": "Allow use of the key",
      "Effect": "Allow",
      "Principal": {
        "AWS": "arn:aws:iam::123456789:role/app-role"
      },
      "Action": [
        "kms:Encrypt",
        "kms:Decrypt",
        "kms:GenerateDataKey"
      ],
      "Resource": "*"
    }
  ]
}
Secrets Management
# Using External Secrets Operator with AWS Secrets Manager
apiVersion: external-secrets.io/v1beta1
kind: ExternalSecret
metadata:
  name: my-app-secrets
spec:
  refreshInterval: 1h
  secretStoreRef:
    kind: ClusterSecretStore
    name: aws-secrets-manager

  target:
    name: my-app-secrets
    creationPolicy: Owner

  data:
    - secretKey: database-url
      remoteRef:
        key: prod/my-app/database
        property: url

    - secretKey: api-key
      remoteRef:
        key: prod/my-app/api
        property: key
High Availability and Disaster Recovery
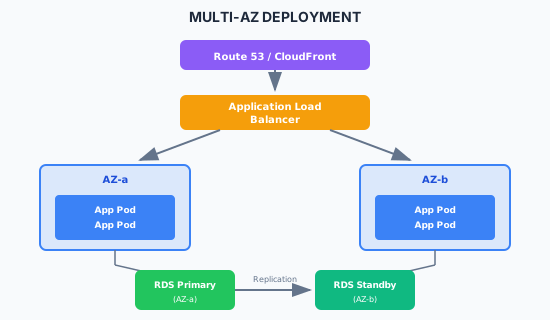
Multi-AZ Architecture
Multi-AZ Deployment Backup Strategy
Cost Optimization
Cost Management Practices
Cost Monitoring
# AWS Budget configuration
Resources:
  MonthlyBudget:
    Type: AWS::Budgets::Budget
    Properties:
      Budget:
        BudgetName: Monthly-Budget
        BudgetLimit:
          Amount: 1000
          Unit: USD
        TimeUnit: MONTHLY
        BudgetType: COST
      NotificationsWithSubscribers:
        - Notification:
            NotificationType: ACTUAL
            ComparisonOperator: GREATER_THAN
            Threshold: 80
          Subscribers:
            - SubscriptionType: EMAIL
              Address: team@example.com
Compliance and Governance
Compliance Frameworks by Cloud
Cloud Security Posture Management
# Checkov policy-as-code example
# .checkov.yaml
framework:
  - terraform
  - kubernetes

skip-check:
  - CKV_AWS_18  # Known exception

hard-fail-on:
  - CKV_AWS_19  # S3 encryption required
  - CKV_AWS_21  # S3 versioning required
- CKV_AWS_145 # KMS encryption requiredCompliance
This section fulfills ISO 13485 requirements for infrastructure management (6.3) and service provision control (7.5.1), and ISO 27001 requirements for cloud security (A.5.23), network security (A.8.20), data protection (A.8.24), and access control (A.5.15).
View full compliance matrix